Security and compliance
Hubject operates critical infrastructure for the eMobility ecosystem. Protecting partner data, securing every transaction, and meeting the regulatory standards that govern them are fundamental to how the business operates.

Security and compliance, built in
Partners depend on Hubject for infrastructure that protects their data, keeps their transactions secure, and stays available when they need it. Meeting that responsibility means securing every part of the platform, complying with the regulations that govern it, and operating in a way partners can rely on. Security, compliance and resilience are not added on top, they are built into how the business operates. This page sets out how Hubject keeps partner data and operations safe, and the standards and regulations behind that commitment.
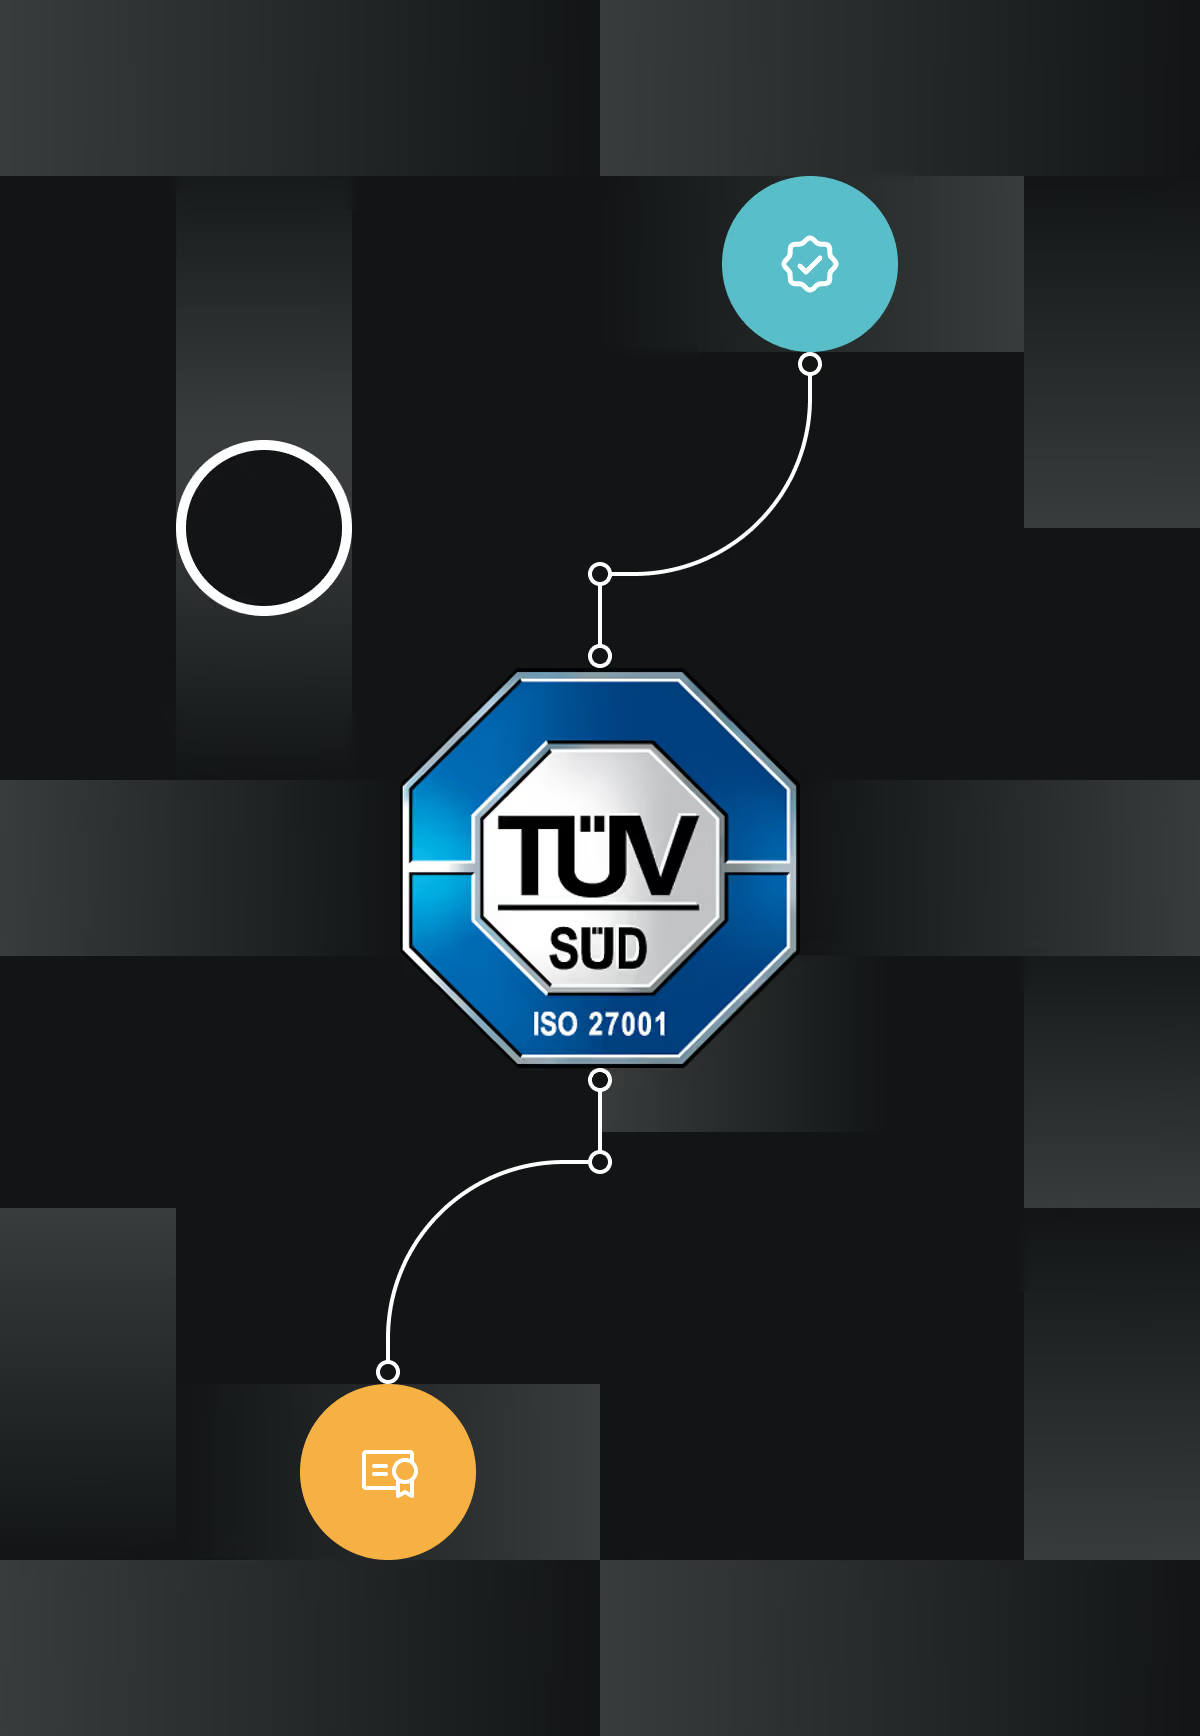
Certified to ISO/IEC 27001:2022
Hubject maintains a certified Information Security Management System (ISMS) in accordance with ISO/IEC 27001:2022, the leading international standard for information security. The certification is issued by TÜV Rheinland and is valid until January 2027. The ISMS is risk-based and subject to regular internal and external audits.
Implementation, operation and support of the Plug&Charge PKI ecosystem and roaming platform for third parties, for the purpose of charging electric vehicles.
An independent body has audited Hubject's security and confirmed it meets the leading international standard. Partners do not have to take Hubject's security on trust, it is certified and re-audited regularly.
Aligned with EU regulatory requirements
Hubject monitors regulatory developments in the European Union, including the NIS2 Directive, and maintains a security governance framework aligned with them. The ISO/IEC 27001:2022-certified ISMS provides a structured framework that supports the requirements expected of essential and important entities under NIS2.
Risk management measures
Incident detection and response
Business continuity and disaster recovery
Supply chain and third-party risk management
Vulnerability management and monitoring
Partners that fall under NIS2 work with a provider whose security governance is already aligned with EU requirements and kept current as they change, which makes their own supply chain obligations easier to meet.
Compliance by design
Compliance is embedded into how Hubject operates, rather than checked after the fact. A structured framework governs how compliance is managed across the business, with clear ownership and regular training to keep standards consistent.
Compliance by design. Compliance is built into Hubject's governance, business processes and service delivery. Internal policies, approval processes and controls support compliance with the legal, regulatory, contractual and industry requirements that apply to the business.
Risk-based governance. A structured compliance framework defines clear roles, responsibilities and oversight to identify, assess and mitigate compliance risk across the organization.
Training and awareness. Employees receive regular compliance training and guidance, so they understand their responsibilities and apply Hubject's standards consistently in their daily work.
Compliance is not left to chance. It is governed, owned and resourced, so partners are working with a business that takes its legal and regulatory obligations seriously.
Doing business responsibly
Hubject holds itself to clear standards of ethical conduct, supported by policies, controls and reporting channels.
Code of Conduct and business ethics. Standards for integrity, respect, managing conflicts of interest and responsible decision-making, expected of all employees.
Anti-bribery and anti-corruption. Policies and internal controls to prevent bribery, corruption, facilitation payments and improper gifts or hospitality, supported by reporting and investigation processes.
Competition law compliance. Clear rules on interactions with competitors, customers and suppliers, covering pricing, information sharing and trade associations, to support fair competition.
Continuous monitoring and improvement. Policies, controls and risk assessments are reviewed and updated as legislation, business activities and best practice change.
Partners are working with a business that holds itself to clear ethical standards and gives anyone a safe way to raise concerns, which is the foundation of a trustworthy long-term partner.
Protecting personal data
Hubject processes personal data in line with the GDPR and applicable data protection law. Data is used only for the purposes it was collected for, stored within the EU, and protected under Hubject’s ISO/IEC 27001:2022-certified ISMS.
Privacy by design. Data protection is built into products and processes from the start, and only the data each service needs is collected.
Clear responsibilities. Where Hubject processes data on behalf of partners, roles and obligations are set out in a data processing agreement.
Rights of individuals. Individuals can access, correct or delete their personal data, or object to its processing. Requests can be sent to Hubject’s Data Protection Officer.
Partners can share data with Hubject knowing it is handled lawfully, kept within the EU, and protected under clear contractual terms.
A structured, risk-based approach
Hubject does not wait for security problems to surface. Risk is identified and assessed on an ongoing basis, controls are put in place to manage it, and the environment is tested regularly to confirm those controls hold. As threats and the business change, the controls are reviewed and updated. The measures below set out how this is done.
Periodic risk assessments
Continuous threat monitoring
Vulnerability management processes
Annual penetration testing
Annual recovery and resilience testing
Defined incident response procedures
Risks are identified and addressed before they become problems for partners. Controls are tested regularly and updated as threats change, so the protection partners rely on keeps pace.
Secure, resilient infrastructure
Hubject's infrastructure is built so that the services partners depend on stay available, and their data stays protected, even if part of the system fails. Critical functions are separated so a problem in one place does not bring everything down, and recovery is tested regularly rather than assumed. The measures below set out how that resilience is maintained.
The services partners depend on are built to stay available, and their data is protected and recoverable if something fails.
Encrypted data transmission and storage
Backup infrastructure in Ireland
Network protection and DDoS mitigation
Regular backup and recovery testing
Production environment hosted on AWS in Frankfurt, Germany
PKI infrastructure operated with Nexus in Stockholm, Sweden
Prepared to detect and respond
Hubject maintains formal procedures for detecting, assessing and responding to security incidents. Incidents are classified, contained and remediated according to defined processes. Where legally required, notifications are made in accordance with applicable regulations, including the GDPR.
Prepared to detect and respond
Hubject maintains formal procedures for detecting, assessing and responding to security incidents. Incidents are classified, contained and remediated according to defined processes. Where legally required, notifications are made in accordance with applicable regulations, including the GDPR.
If an incident occurs, it is contained and handled quickly through a defined process, and partners are notified where they need to be.
Security documentation
Key security and compliance documents are available to download.
ISO/IEC 27001:2022 Certificate
Plug&Charge PKI Certificate Policy
Build on infrastructure you can trust
Hubject treats the security of partner data and operations as fundamental. Talk to the team to learn more.